
Network security / identity and authentication
Identity & Access Management Platform
Yuqi Intelligent starts from identity sources, entry points and business permissions to assess and design authentication, MFA, policy decisions and log boundaries across wired, wireless, VPN and application entries, so the enterprise knows who is accessing, why access is allowed and how to trace incidents.
01 Define the problem first
Many entry points, one identity model
Enterprise accounts are scattered across directories, wireless, VPN and applications. The hard question is not whether a login page exists, but whether identity, devices, entry points, permissions and logs still align after people change roles.
An identity platform should reduce shared accounts, duplicate accounts, temporary access and untraceable connections. During design, it can connect naturally to Wireless coverage, Enterprise networking and SD-WAN or Internal Network Security & Access Control, while each system’s authentication, authorisation and admission ownership still needs to be stated separately.
Accounts are scattered and their lifecycle breaks
Directories, wireless, VPN and business systems maintain accounts separately, leaving permissions behind after transfers, departures or partner work ends.
Authentication does not automatically grant access
Confirming an account is correct is not enough if role, resource, device state and time conditions are absent from authorisation and admission decisions.
Entry points and logs tell different stories
Wired, wireless, VPN and application access records cannot be correlated, making it difficult to reconstruct who accessed what and where after an incident.
02 Identity and admission architecture
Unify identity across different entry points
A unified identity source does not force every device and application onto one protocol. First clarify identity lifecycle, parallel entry points, policy decisions and log ownership; SSO, RADIUS and directory integration depend on device and application support.
The identity source and lifecycle establish the subject first. Employee networks, wireless access, VPN and business applications enter authentication and policy decisions in parallel, then produce permissioned access results and auditable logs; the diagram is not a user sequence or a project deployment topology.
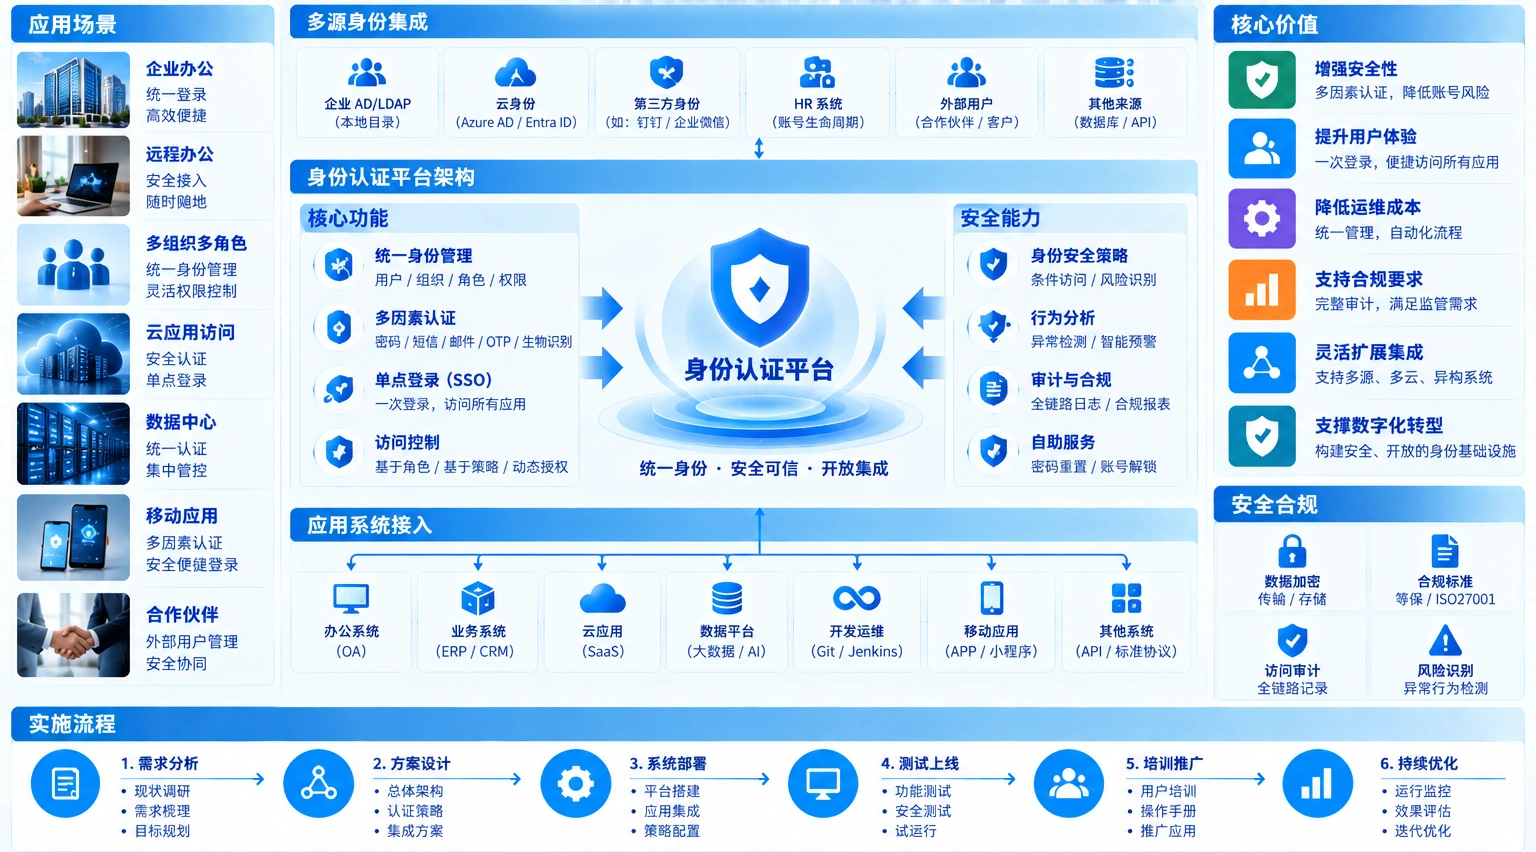
The diagram explains identity sources, entry points and ownership boundaries. It is not a project topology, protocol combination or user sequence; integration scope must be confirmed against equipment, application interfaces and tests.
03 Authentication and admission boundaries
Identity, permissions and access have distinct roles
One platform may participate in several decisions, but three questions cannot be collapsed into “unified authentication”. The supported protocols, deployable policies and maintenance ownership must be clear at design and acceptance.
Authentication
Confirm who you are using an account, certificate, MFA or another agreed factor.
Authorisation
Confirm what you may access, deciding scope by role, resource, time and business need.
Admission
Confirm whether the current entry point may pass, using device, network, location, state and policy to allow, limit or deny.
04 Identity authentication services
What Yuqi Intelligent can deliver
Scope follows the current state, equipment capability, business priorities and implementation window, covering assessment, design, selection, supply, deployment, integration, piloting, migration, handover and training; support follows the agreed scope.
Identity and entry assessment
Inventory employees, guests, partners, administrators, endpoints and existing accounts, then confirm real dependencies across wired, wireless, VPN and business entry points.
Authentication architecture and product selection
Define an explainable architecture and selection boundary around identity sources, MFA, directories, RADIUS, SSO, device capability and log requirements.
Policy and role design
Model authentication, authorisation and admission separately, defining roles, resources, device state, time conditions, exceptions and revocation ownership.
Deployment, integration and pilot
Deploy the platform, configure interfaces and integrate network equipment and applications, then validate success, failure, exceptions and rollback from a representative entry point.
Migration, go-live and handover
Migrate accounts and entry points in the agreed window, retaining change records, test evidence, configuration backups and rollback-capable procedures.
Training and operational support
Deliver account-role matrices, interface lists, configuration tests and operations records, with training and follow-up support as agreed.
05 Phased implementation and client handover
Roll out in phases for maintainable delivery
Identity authentication affects real user sign-in, device access and business continuity. Pilot a representative entry first, validate success, failure, exceptions, logs and rollback, then expand within the migration window and hand over configuration, tests and ownership.
Current-state and identity inventory
Map identity sources, people types, lifecycles, entry points, device conditions, resource scope and existing account ownership.
Target policy and selection
Confirm authentication methods, MFA, directory or RADIUS / SSO interfaces, role permissions, admission boundaries and log requirements.
Pilot integration and migration
Validate employee, guest, administrator, unknown-device and exception scenarios at one representative entry point before expanding in phases.
Acceptance, handover and support
Check authorisation results, logs, configuration, rollback, records and training so account and access relationships remain maintainable.
06 Client delivery result
Deliver more than authentication: deliver maintainable access relationships
Deliverables follow the project scope and acceptance conditions. When network entry points and policy also need review, connect to Wireless coverage or Enterprise networking and SD-WAN, recording interfaces, configuration, logs and maintenance ownership in the operations documentation.
- Identity-source, account-role and lifecycle matrix
- Entry points, interfaces, authentication methods and device-support list
- Policy, configuration, testing, migration and rollback records
- Log audit, operations records, training and ownership handover
07 Frequently asked questions
Clarify entry points, protocols and ownership boundaries first.
Does an identity platform only manage wireless access?
No. Depending on site equipment and protocol support, it can connect wired, wireless, VPN, branch and business-application entry points. The focus is establishing identity, entry, permission and log relationships.
Can SSO, RADIUS, directories and MFA all be unified automatically?
Do not promise this in advance. First check protocol, interface and policy support across directories, network equipment, wireless controllers, VPN, applications and platforms, then define integration scope, pilot method and manual boundaries.
Should employees, guests and partners share accounts?
Usually not. Design accounts, authentication and permissions by identity type, access scope, duration, approval and audit requirements, with revocation paths for departures, ended partnerships and temporary grants.
Next step / IDENTITY REVIEW
Start with an entry inventory or one access problem.
Tell us about identity sources, network entry points, application scope and recurring access problems. We will define the next step around equipment support, policy boundaries, pilot windows and delivery ownership.